Governance, Risk,
and Compliance (GRC) for regulated and audit-heavy teams.

From requirements to proof – one traceable flow. Riskflow Asset is asset-centered GRC. It connects asset context, assessments, controls, and evidence so teams can turn regulatory, legal, contractual, and internal requirements into clear control scope and audit-ready proof.

What makes Riskflow Asset different: asset-centered GRC

Traditional GRC often starts with catalogs, questionnaires, and isolated control work. Riskflow Asset starts with the asset landscape the requirements actually affect.


By keeping requirements, asset context, controls, ownership, and evidence connected, teams can see what applies, what is missing, and what is proven – even as systems, services, and dependencies change.

Asset-centered GRC is not another asset database. It is a way to make requirements operational through asset context.

Problem

Why today’s
GRC hurts

Requirements change. Asset landscapes change. Internal controls evolve. But in many organizations, these things do not stay connected.

That is when GRC turns into spreadsheets, folders, tickets, and one-off answers. Teams lose track of what applies, what is covered, who owns it, and what can actually be proven.

Requirements drift away from operations

Regulatory, legal, contractual, and internal obligations often live far away from the assets, services, and processes they affect.

Control scope becomes unclear

Teams struggle to see which controls apply where, why they apply, and what still needs action.

Evidence shows up too late

Proof gets collected at the end instead of staying attached to the work throughout the process.

The same work gets repeated

Assessments, customer requests, and audits often trigger duplicate effort because context is not reused.

Challenge

What modern GRC must deliver

Modern GRC should do more than document obligations. It should make them operational – by connecting requirements, asset context, controls, evidence, and live status.

Translate requirements into controls

Turn external and internal obligations into clear, actionable control scope.

Continuous compliance and assurance

Keep requirements, controls, and evidence connected over time.

Show live status

Make gaps, overdue reviews, and progress visible without manual reporting loops.

Reduce repeat work

Reuse shared context, mapped controls, and existing responses wherever possible.

Operational control visibility

See gaps, ownership, and status across changing asset landscapes.

and much
more …

Solution

Why Riskflow Asset
was built for this

Riskflow Asset was designed for regulated and audit-heavy environments where requirements need to become operational, traceable, and provable.

Built in Europe

Designed for strong regulatory environments and high expectations around privacy, security, and auditability.

Integrate, don’t replace

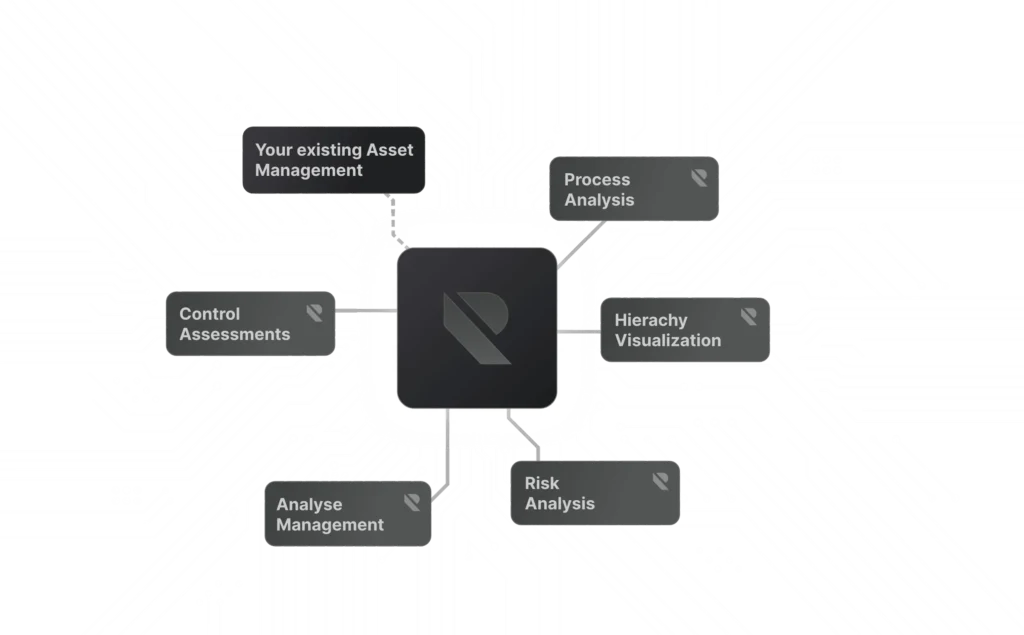
Riskflow Asset works with the systems you already use instead of forcing another disconnected asset silo.

From requirements to controls – end to end

Riskflow Asset connects requirements, asset context, control scope, responses, and evidence in one model.

Traceable by design

See where context comes from, how it flows, and why a control applies.

Automation that stays understandable

Reduce manual work through structure and inheritance without losing transparency.

How Riskflow Asset works

GRC, built for today’s regulated teams

Step 1

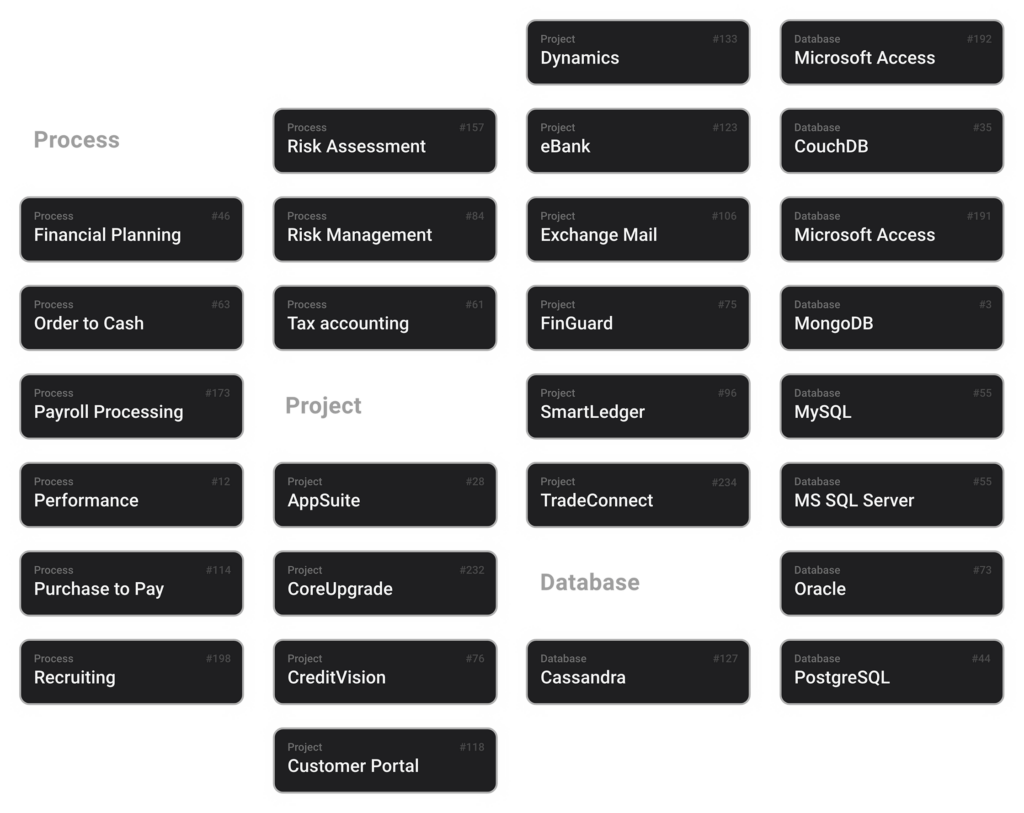
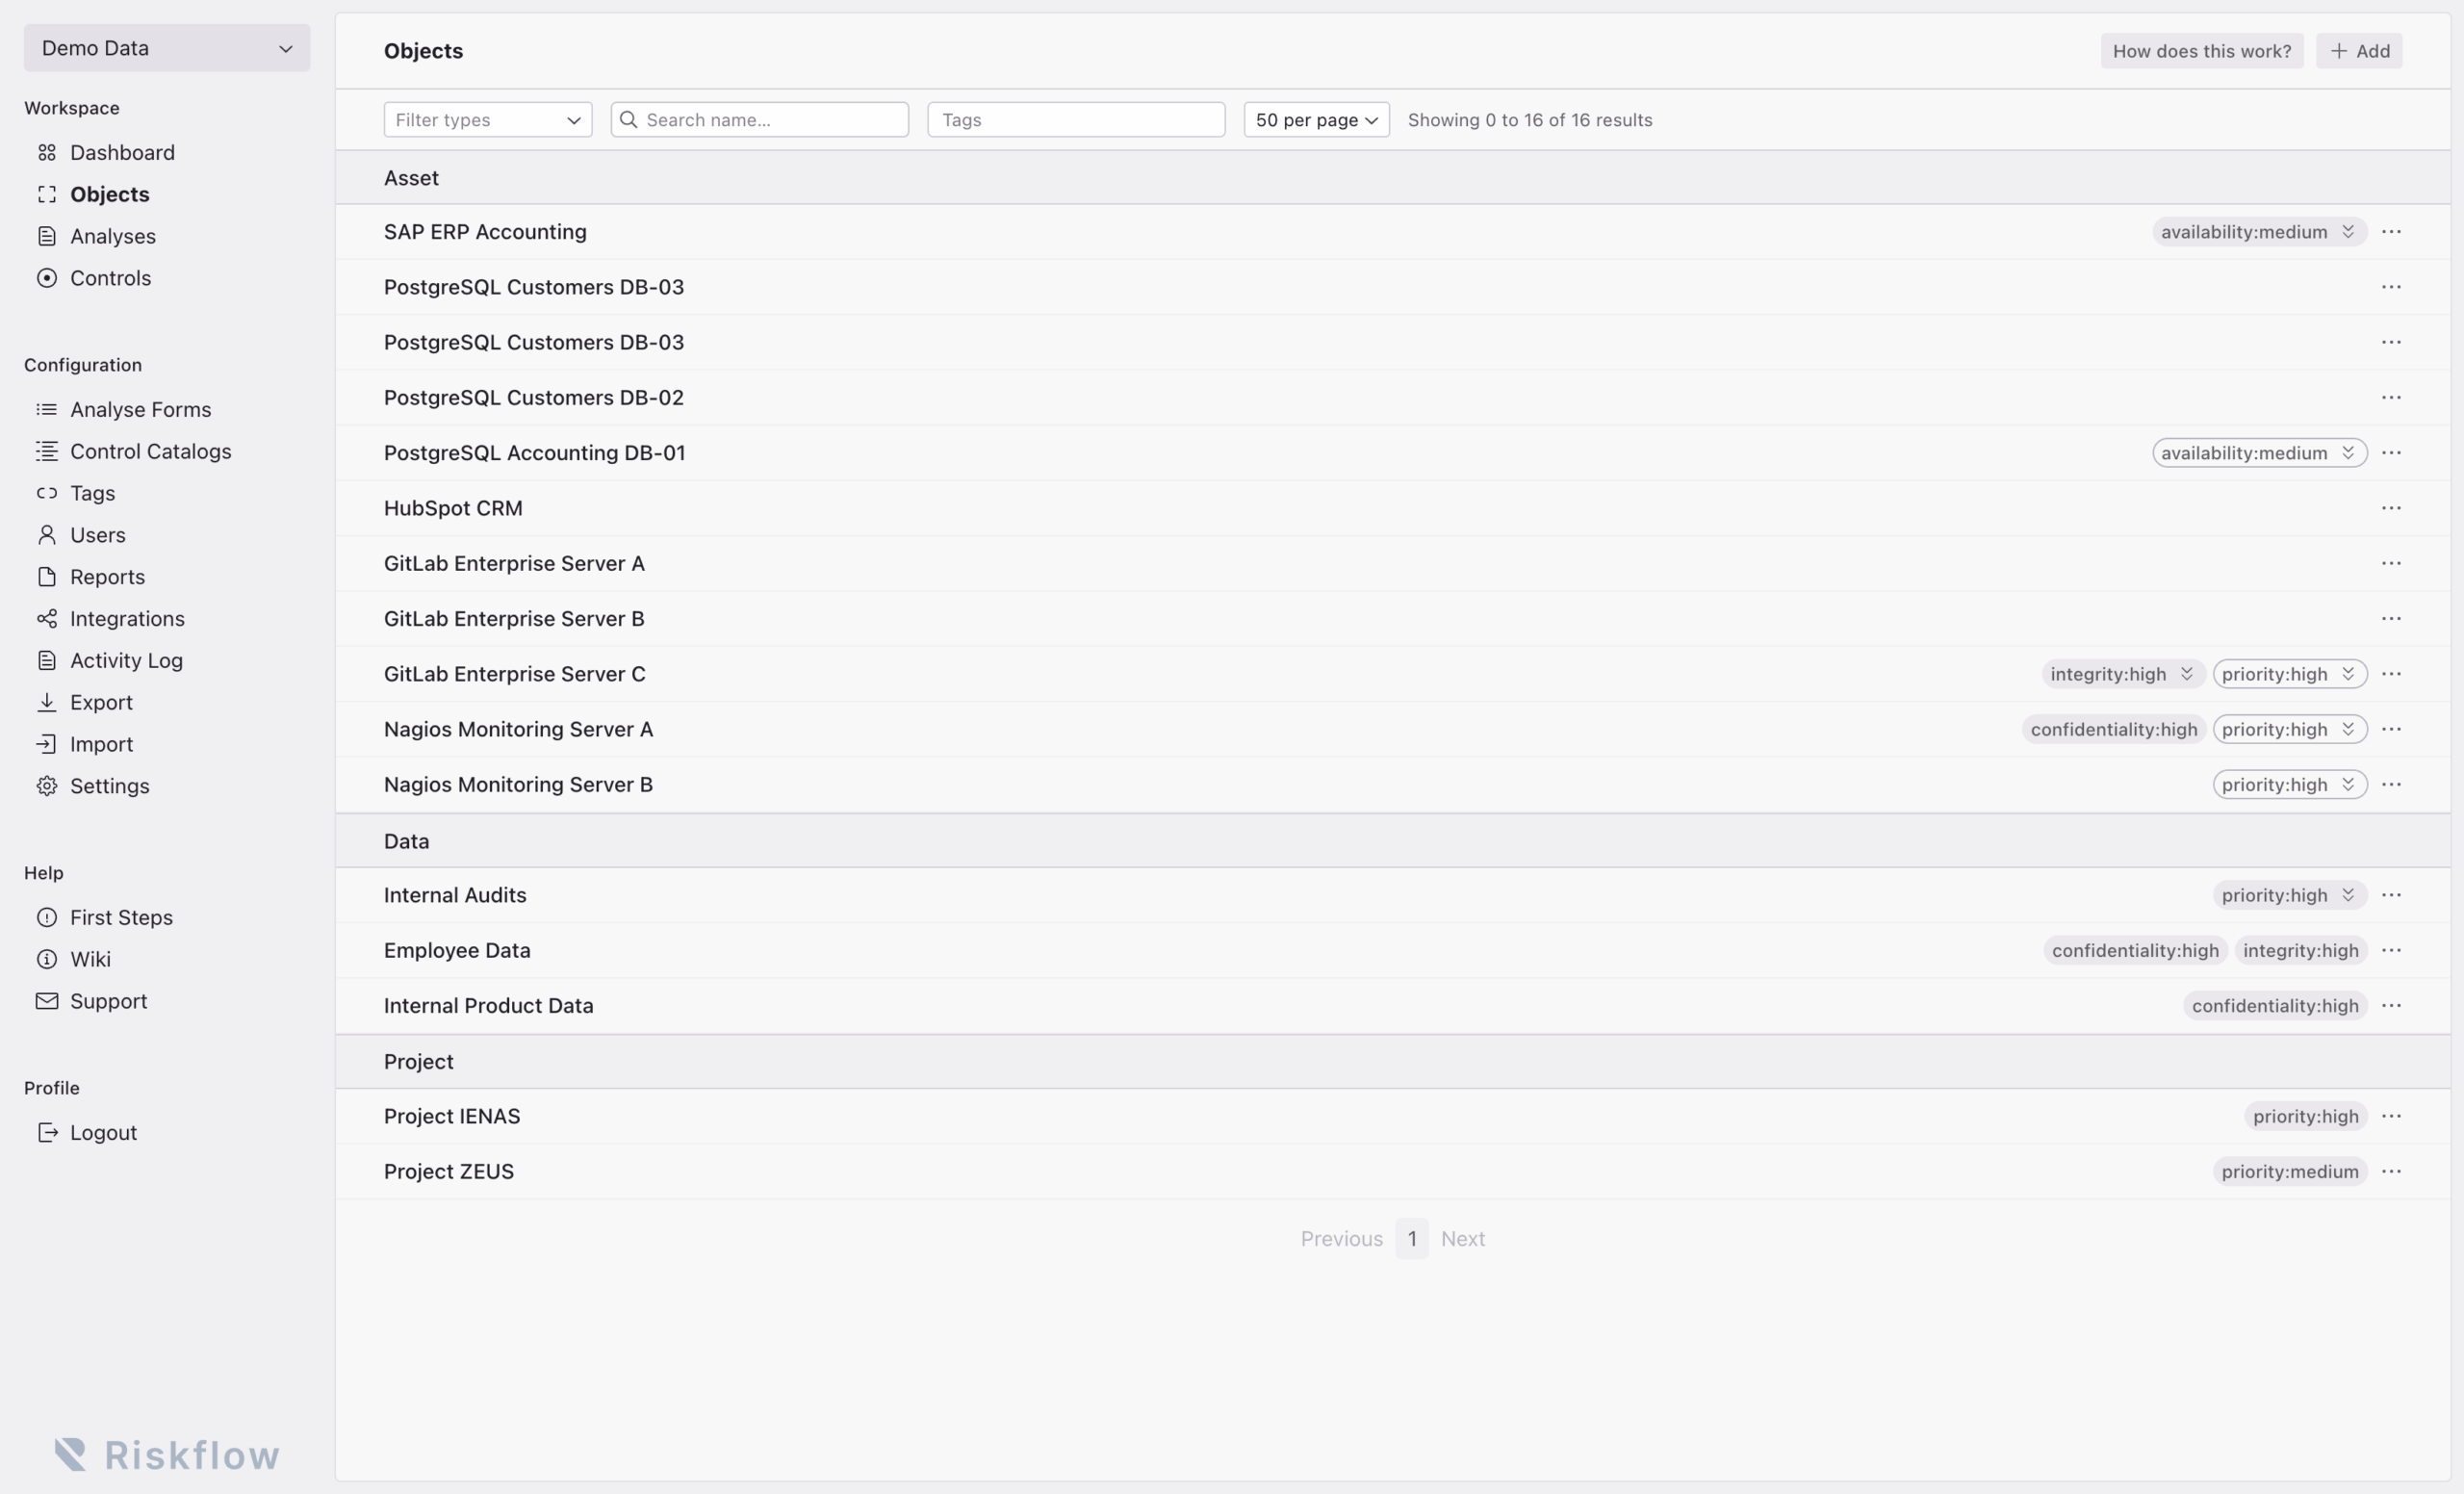
Bring in your asset landscape

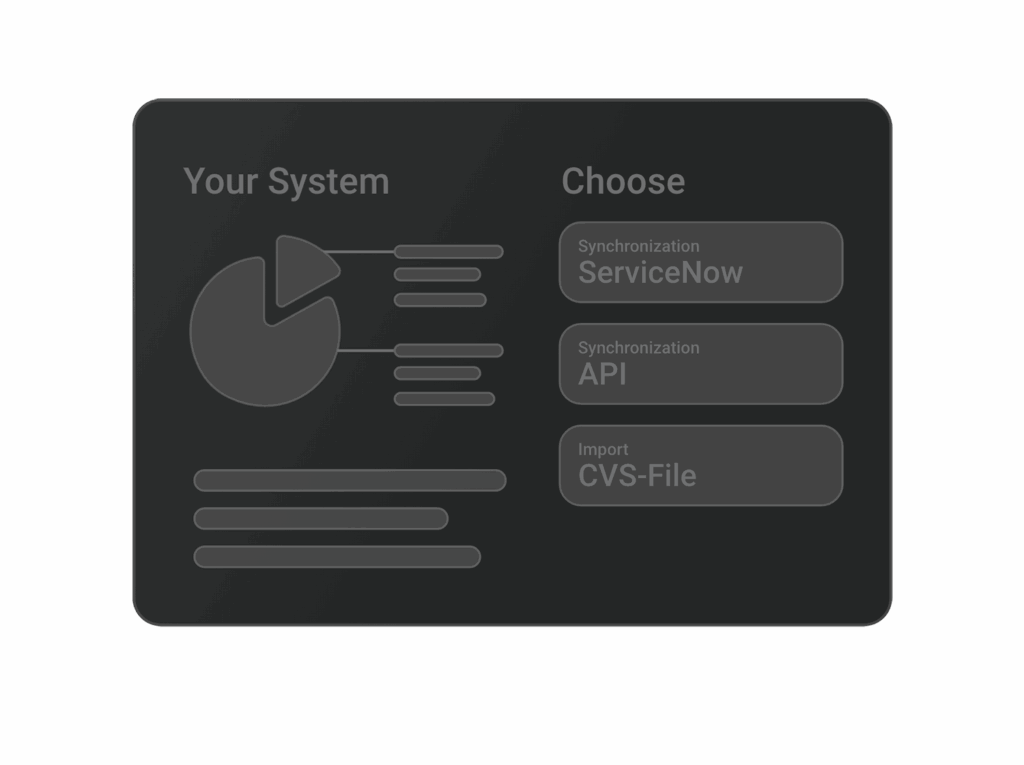
Keep your assets in the systems you already use. Riskflow Asset syncs the context it needs.

Step 2

Build structure and context

Structure assets, apply tags, and model dependencies so relevant context stays connected.

Step 3

Run assessments where they belong

Run assessments, map controls, and see which requirements apply where.

Step 4

Map controls with precision

Apply controls based on structure and relevance, not on broad assumptions or manual distribution.

Result

See the full picture

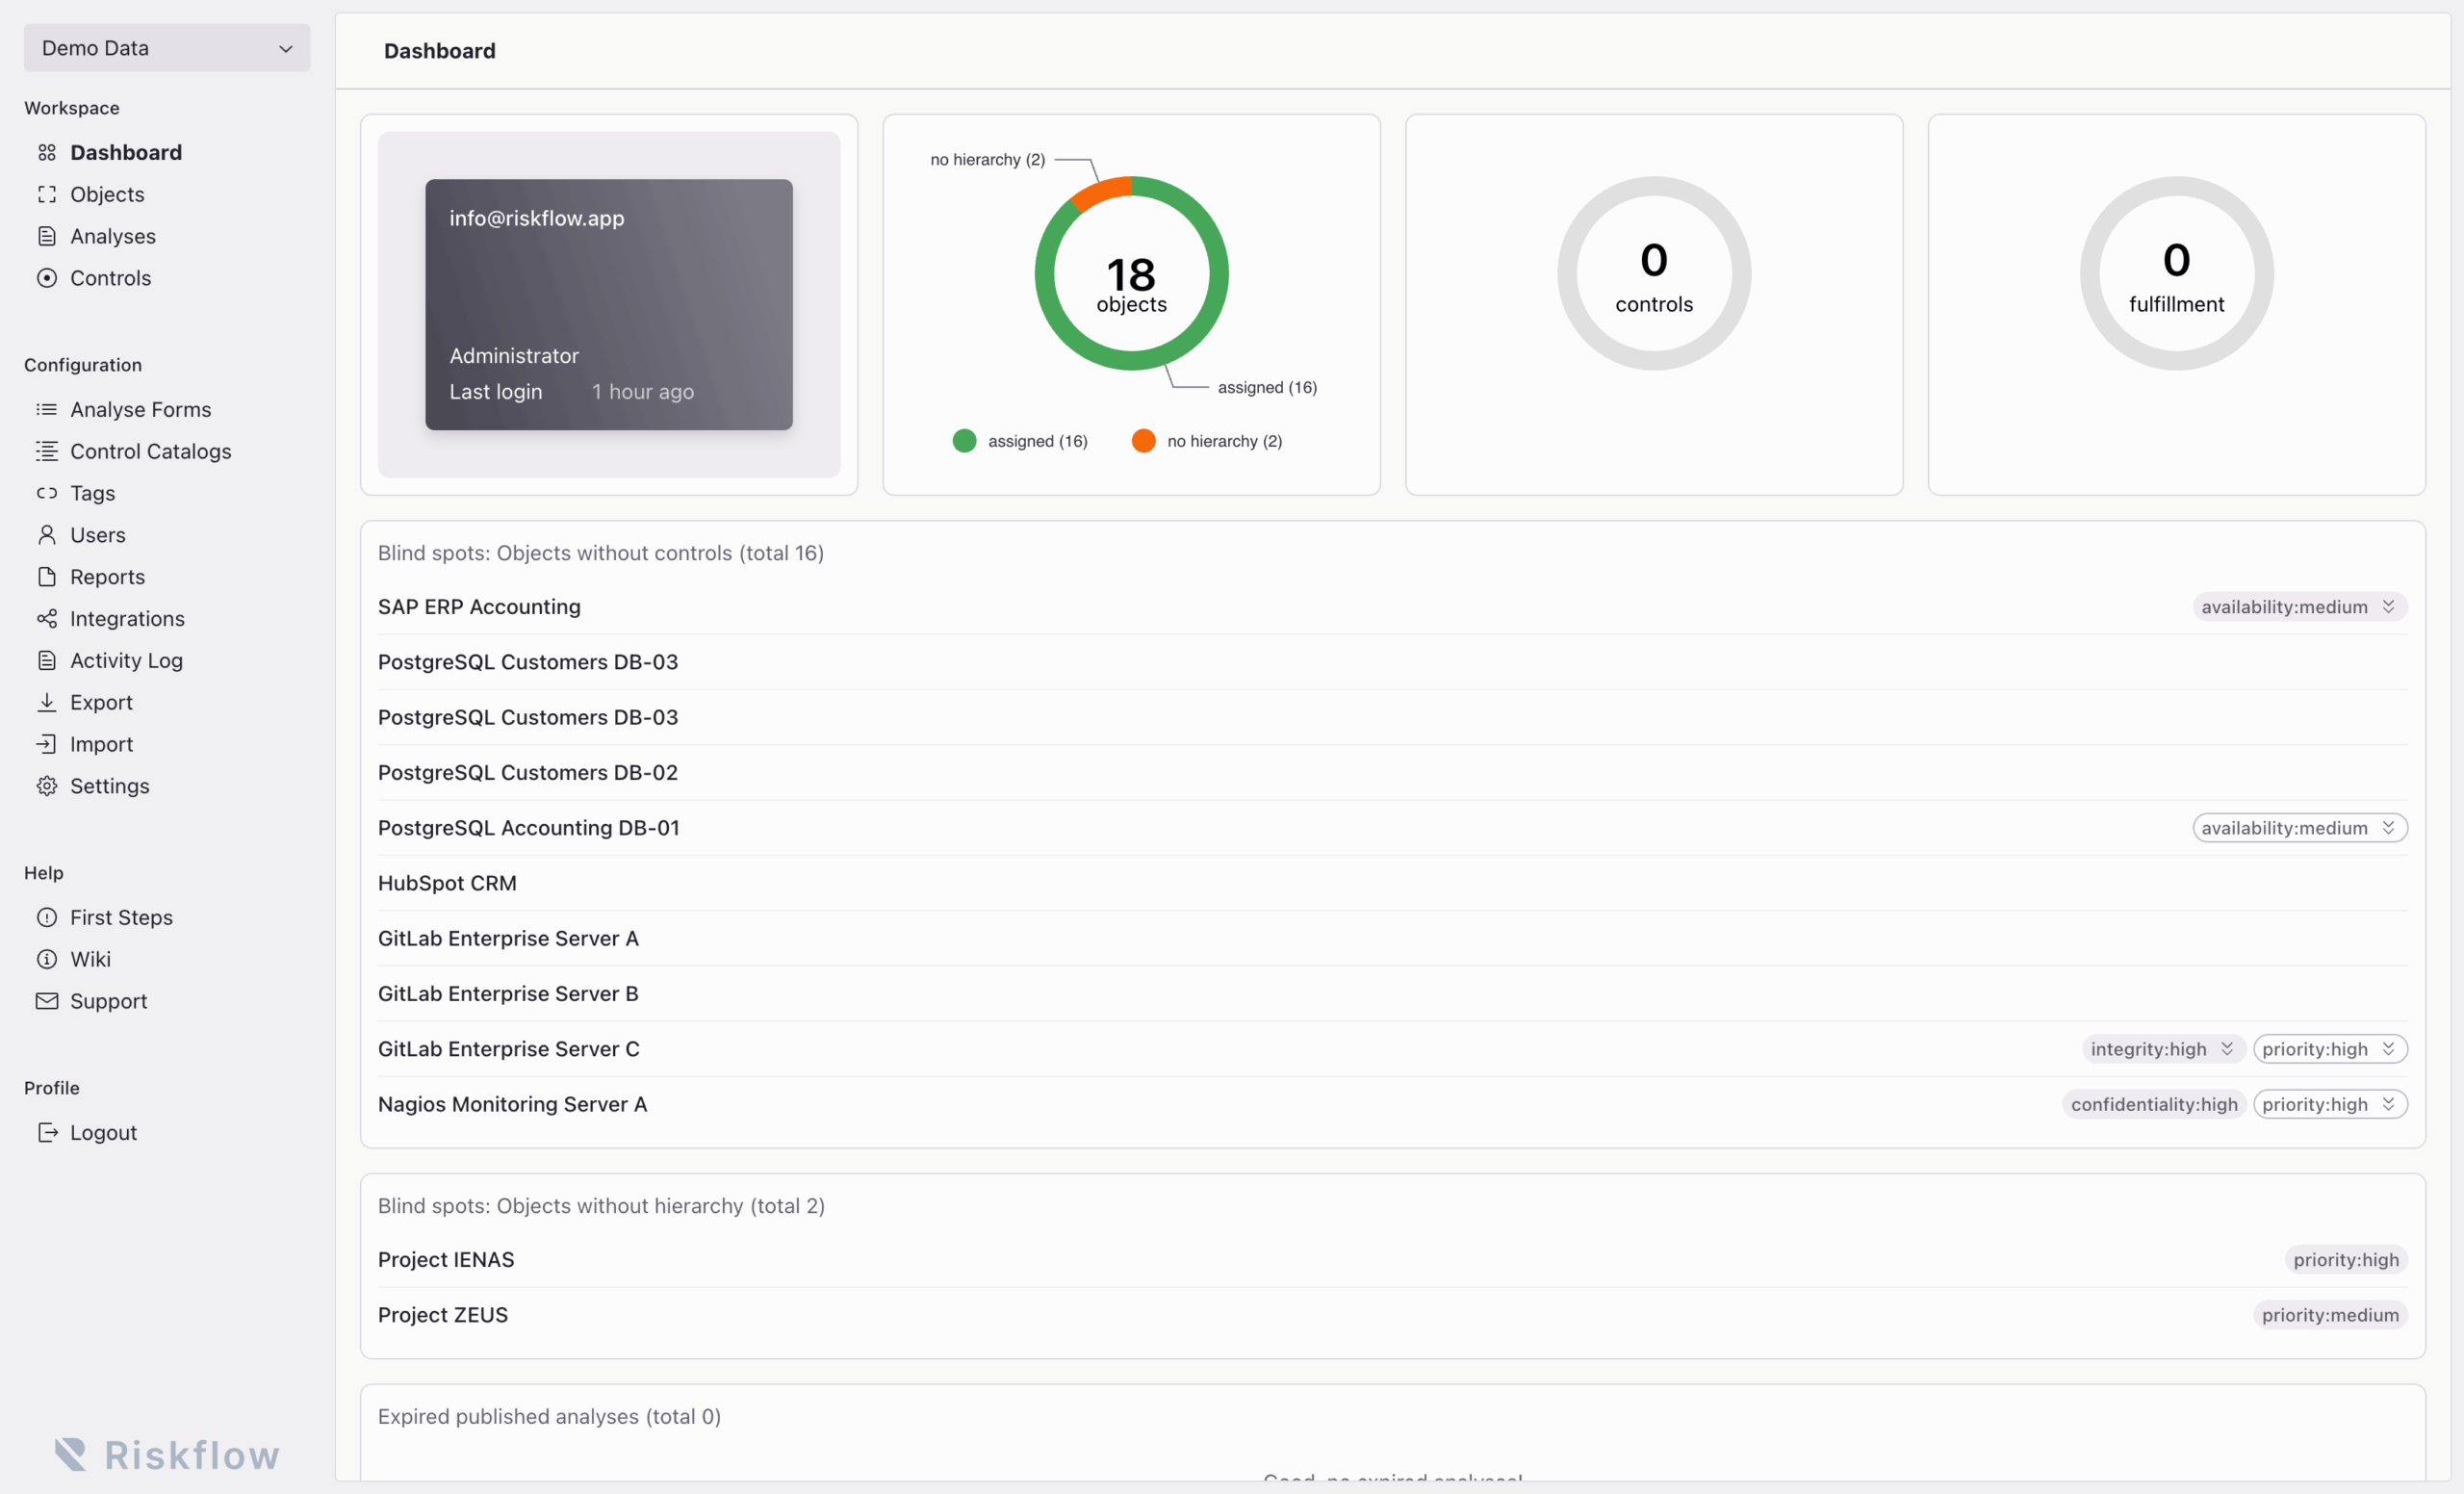
Get a usable overview of control coverage, open gaps, impacted areas, and next actions.

User Interface

Riskflow Asset in action

Features

Built to turn requirements into proof

Riskflow Asset helps teams operationalize regulatory, legal, contractual, and internal requirements by connecting asset context, controls, ownership, and evidence in one system.

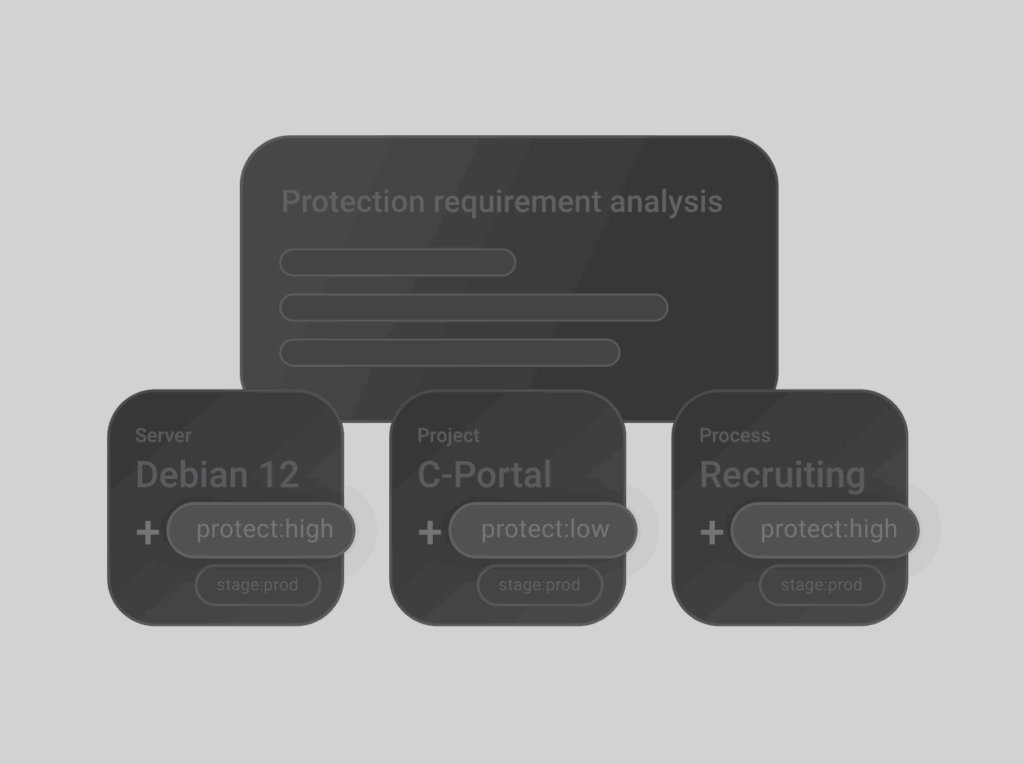
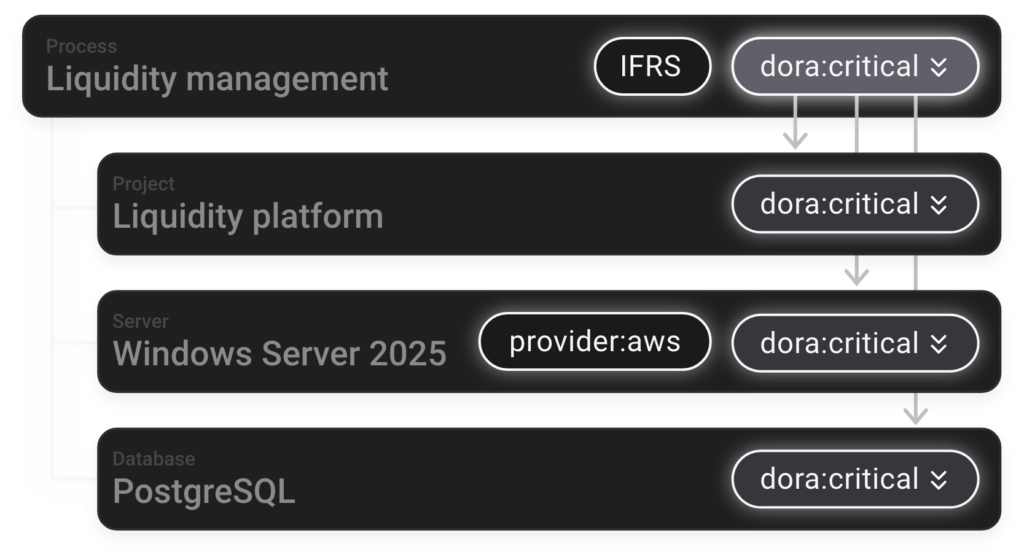
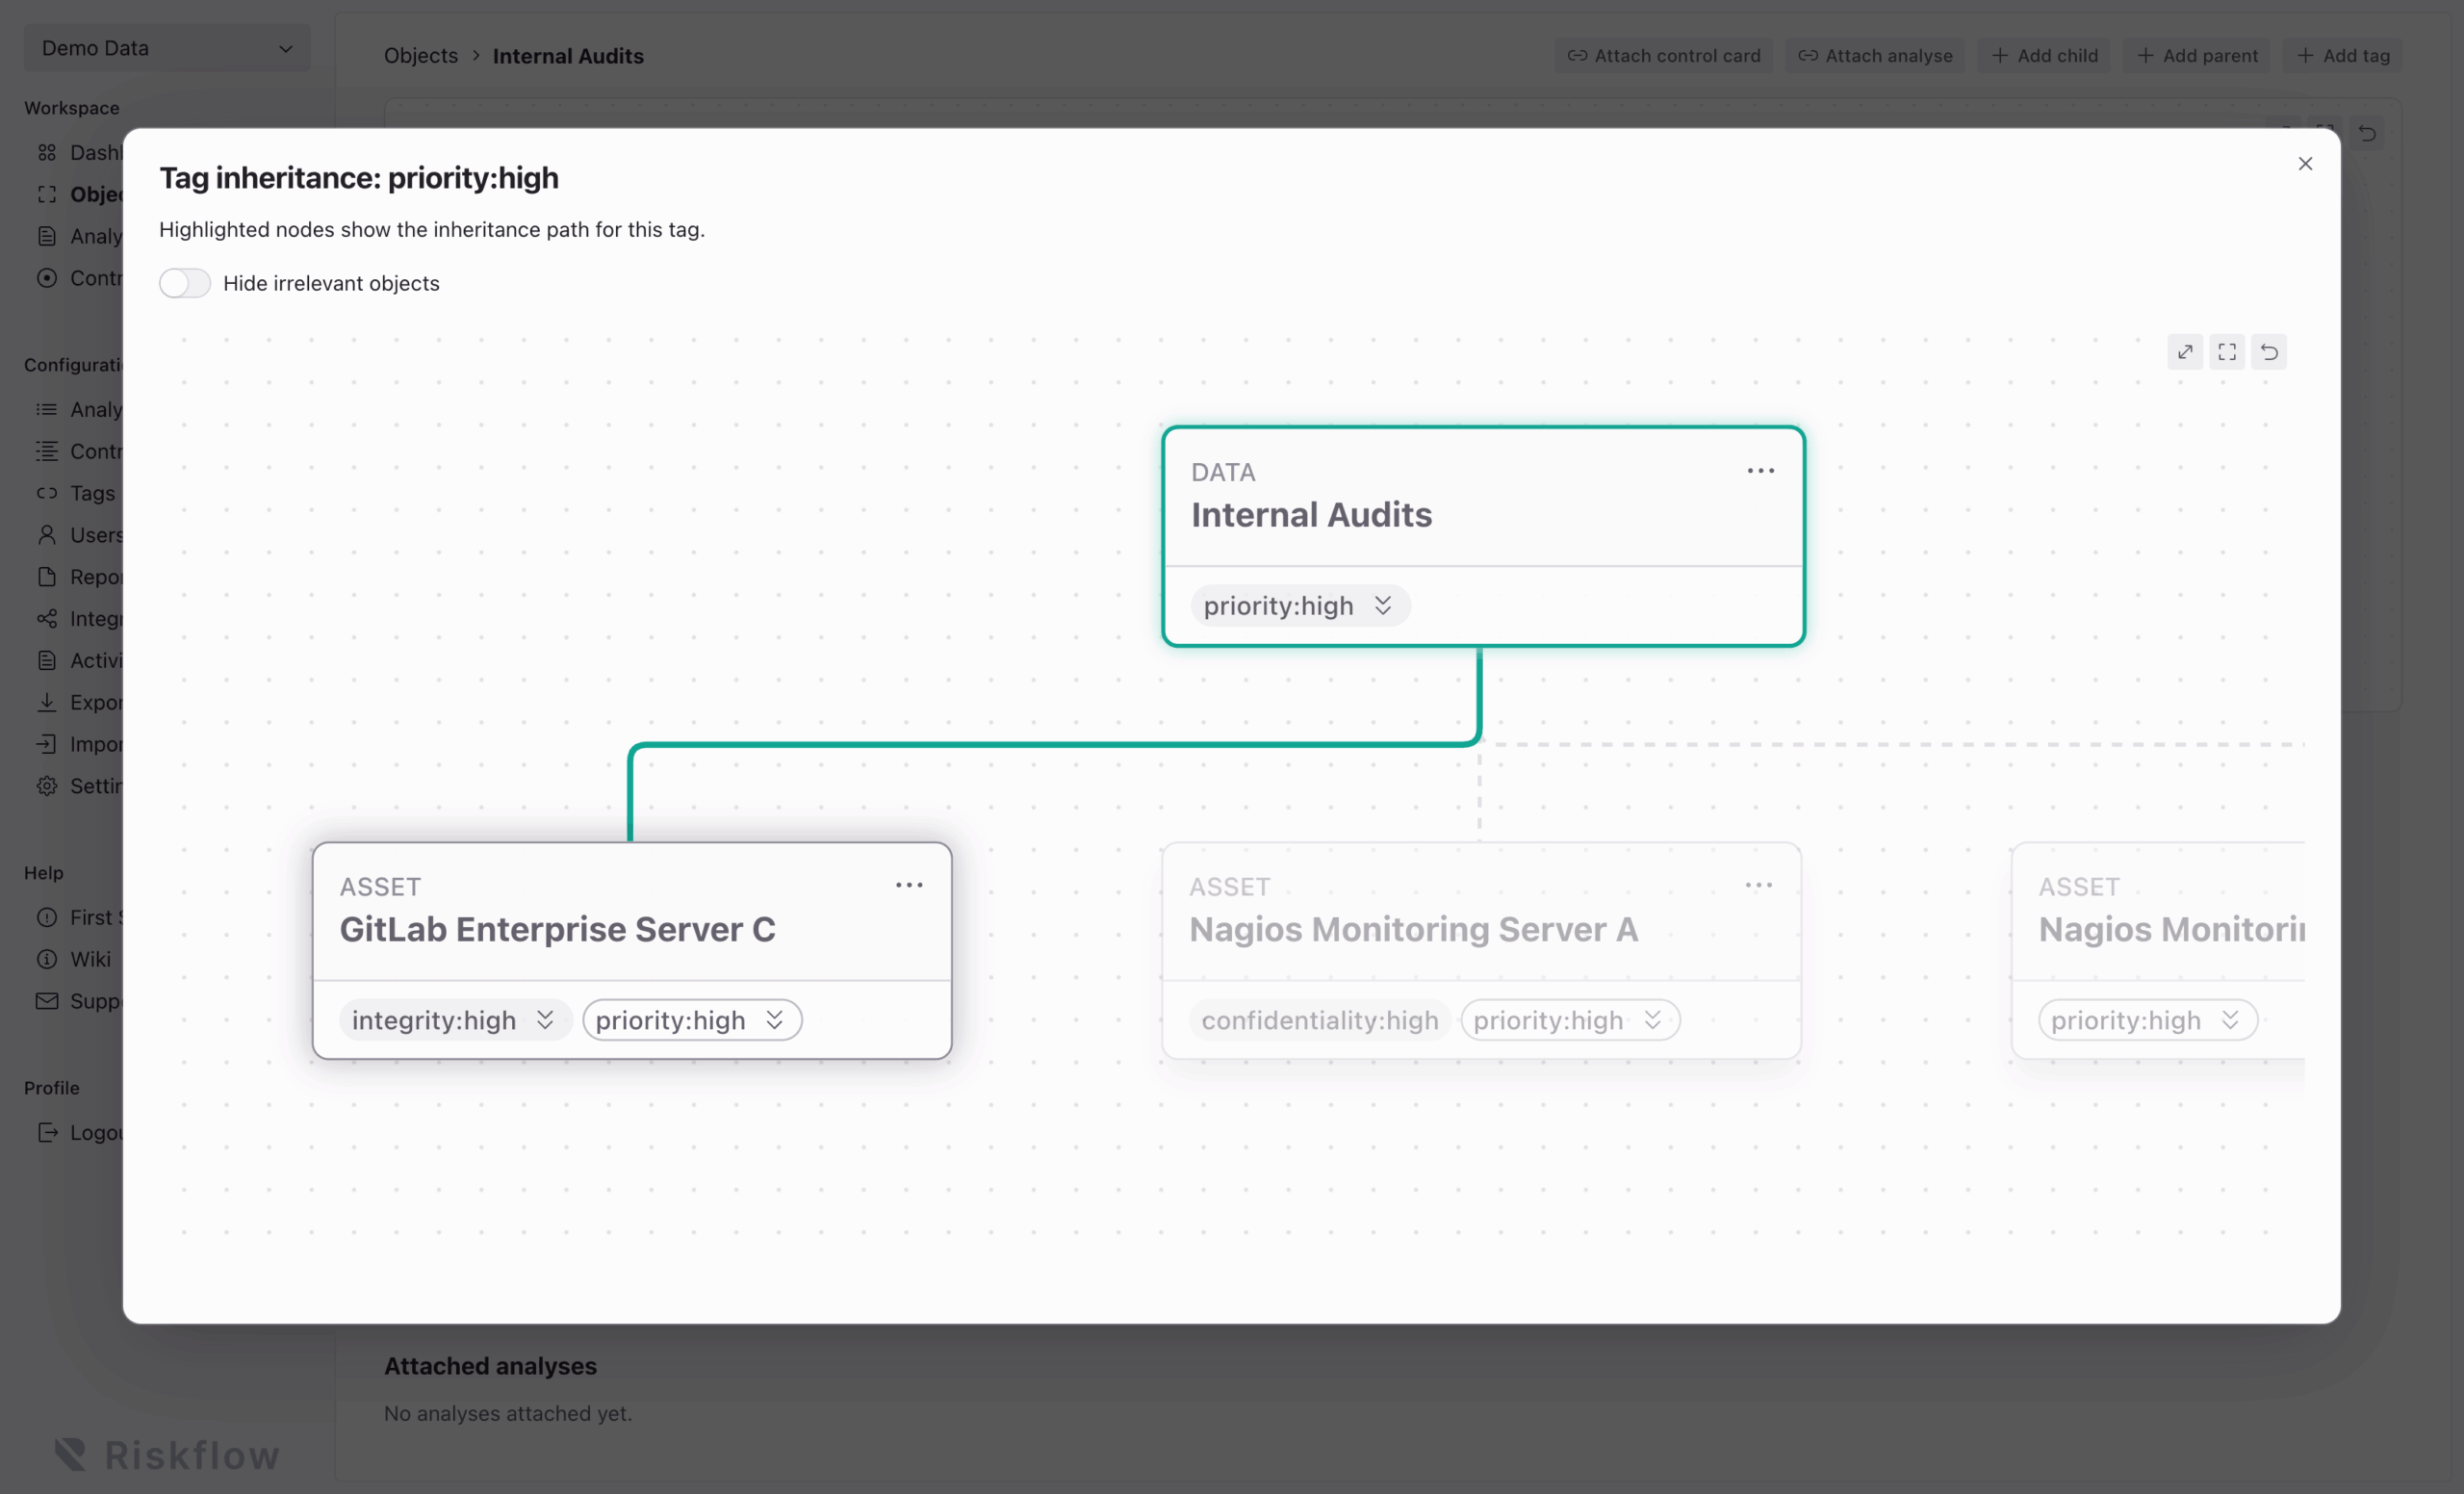
Tagging System

Apply context once
and reuse it

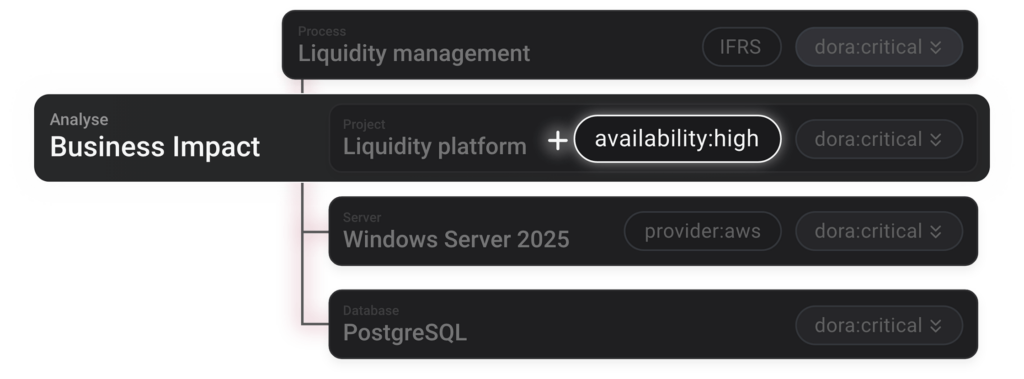
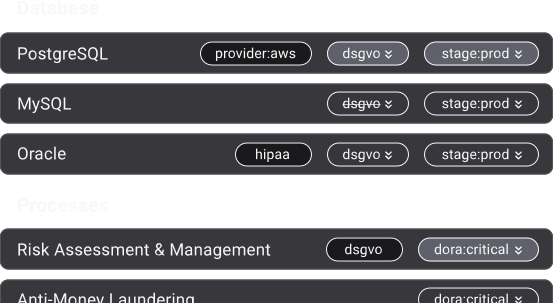
Tags carry requirement-relevant context across connected assets. This keeps control scope consistent and reduces the need to recreate the same logic object by object.

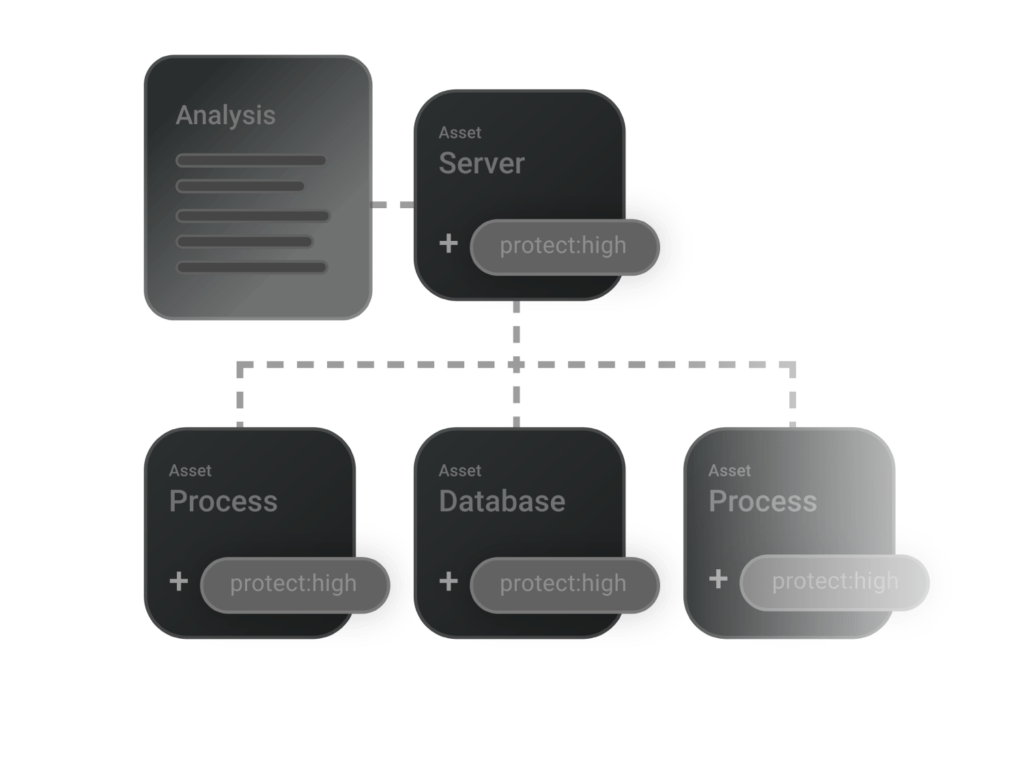
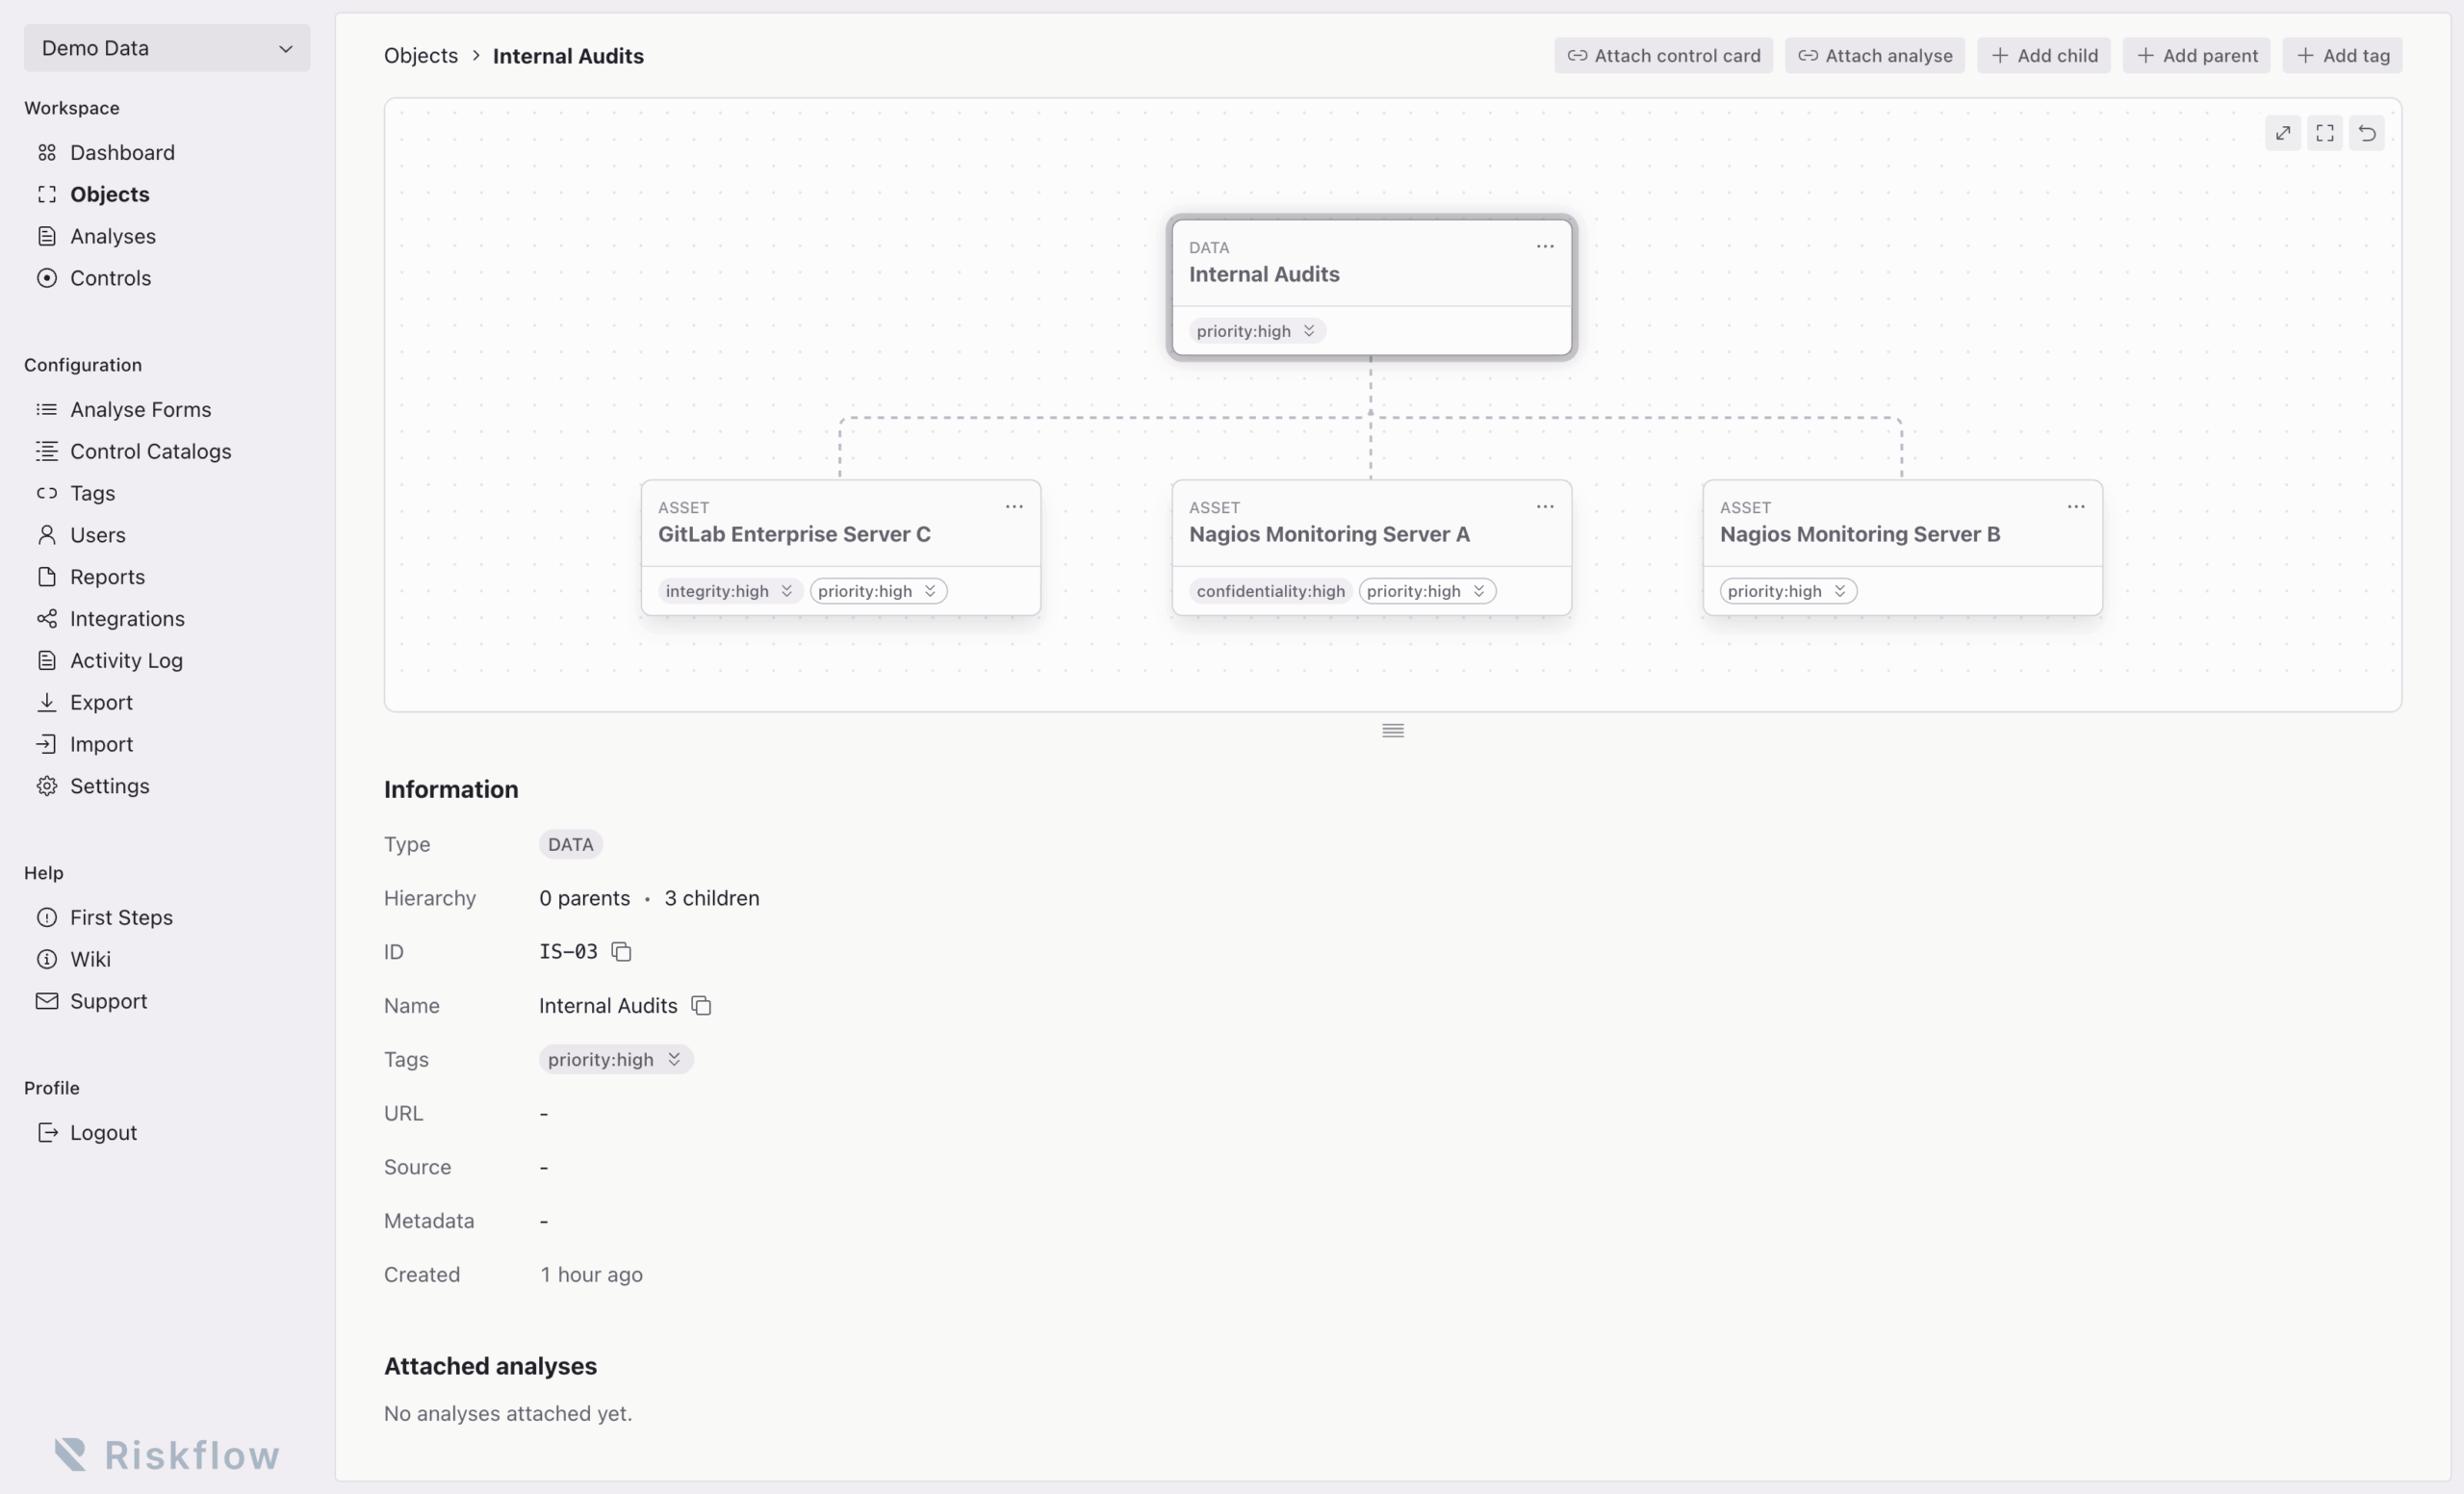
Tree View

See structure and dependencies at a glance

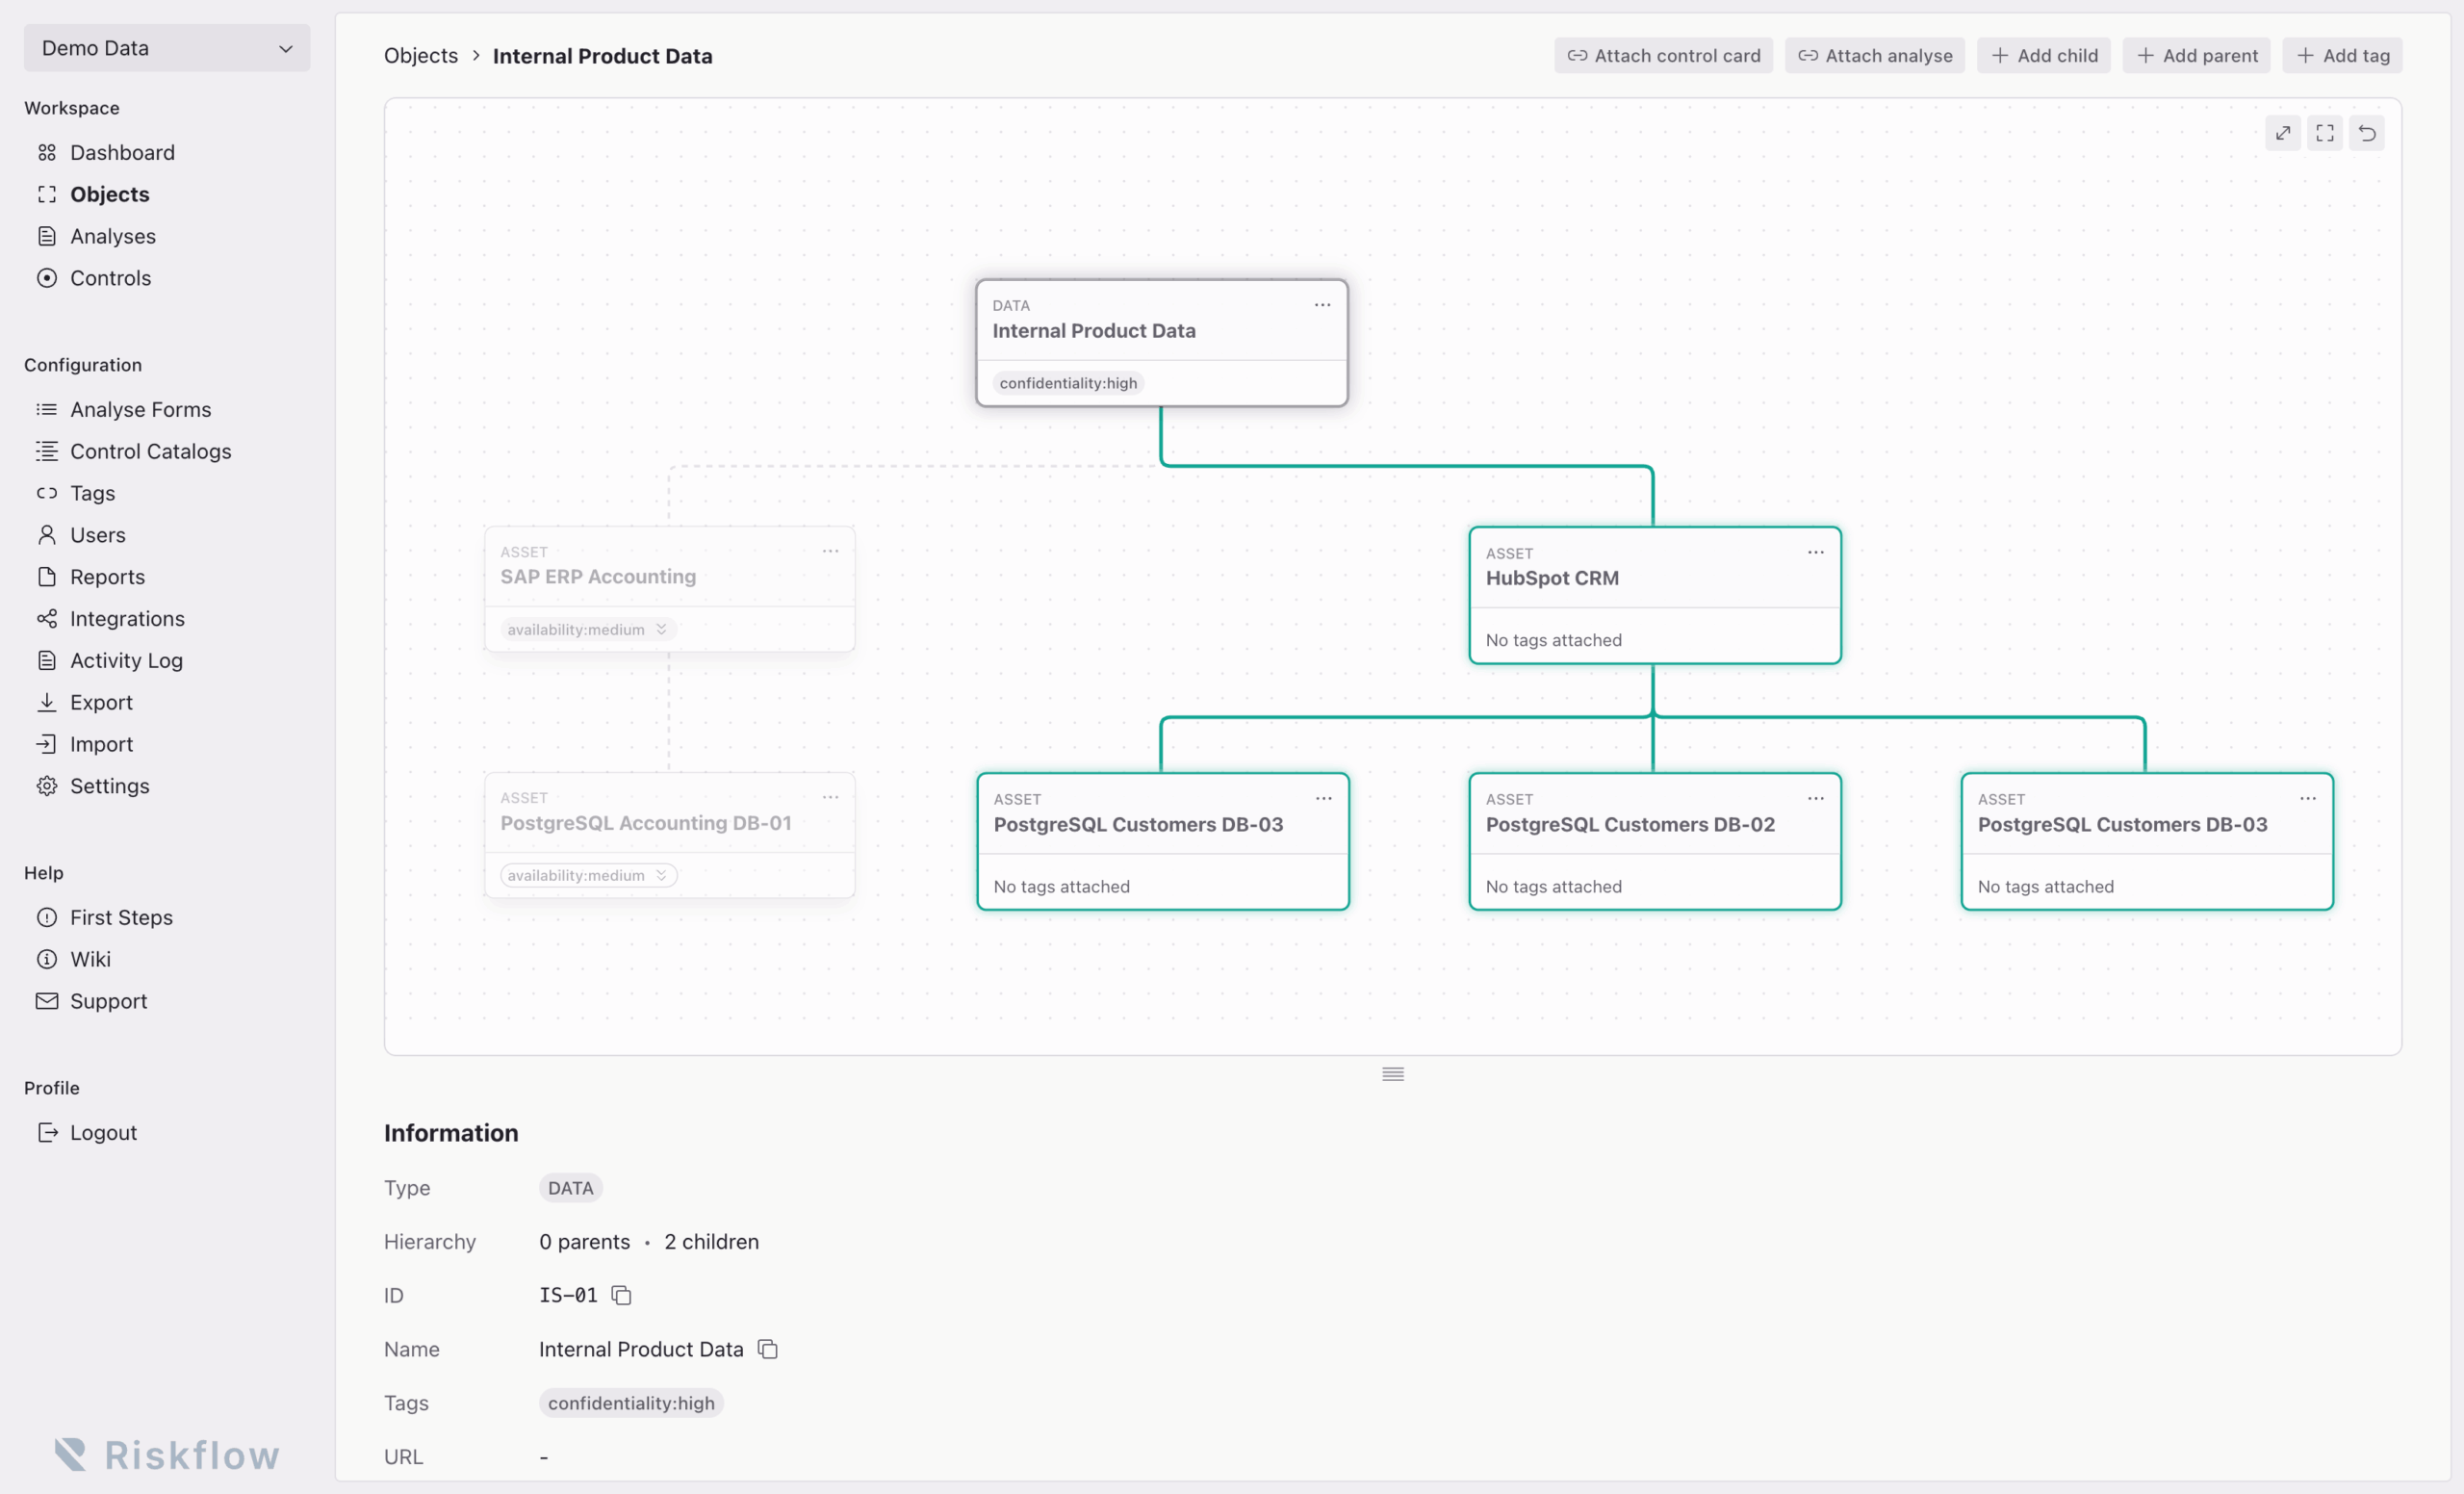
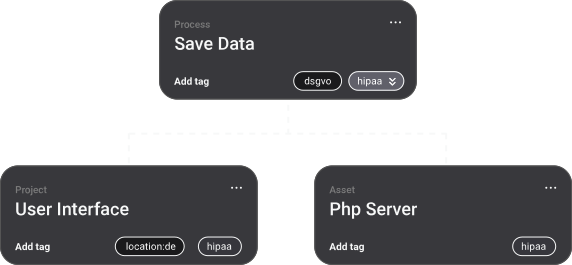
Understand hierarchies, dependencies, and ownership in one view. That makes it easier to see where requirements land and how changes affect the wider environment.

Assessments & Form Builder

Turn requirements into operational input

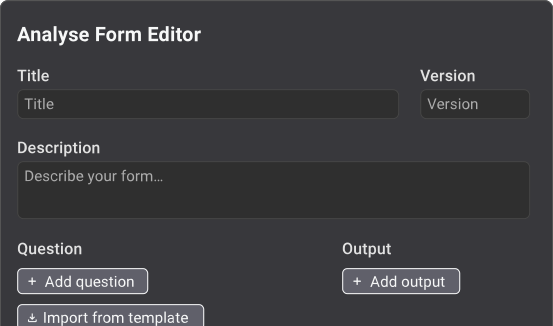
Create assessments, use templates, and attach them where they belong. Results stay connected to the asset context and can directly support downstream control work.

Control Assessment Hub

Keep control work and evidence in one flow

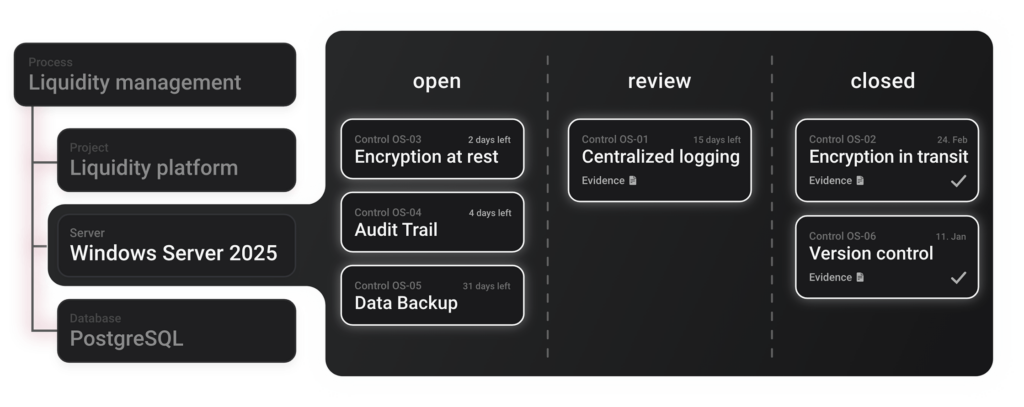
Manage control responses, evidence, and collaboration in one place. This keeps proof attached to the work instead of reconstructing it at the end.

How do we save you from filling out countless controls?

Own your data

Keep your source systems as
the source of truth

Riskflow Asset is not another redundant asset database. It uses the systems you already rely on, adds traceable control logic on top, and helps you avoid managing the same data twice.

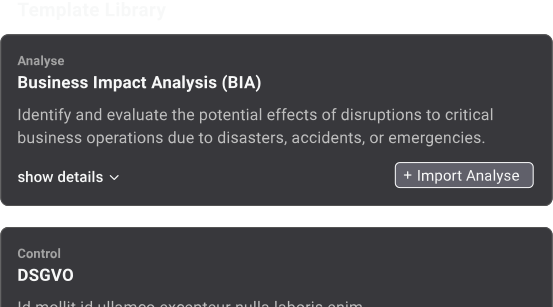
Template Library

Start faster with reusable building blocks

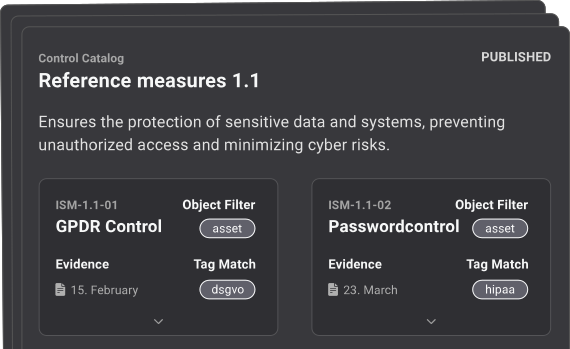
Use predefined assessments and control catalogs for common frameworks, then adapt them to your environment. That shortens setup time without forcing a rigid model.

Recertification

Support recurring reviews without losing momentum

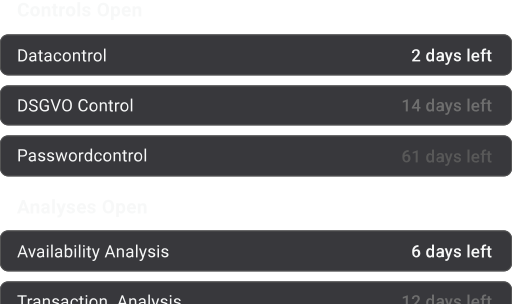
Automatically reopen controls and assessments on schedule, keep review cycles moving, and make recurring compliance work easier to manage over time.

Insights

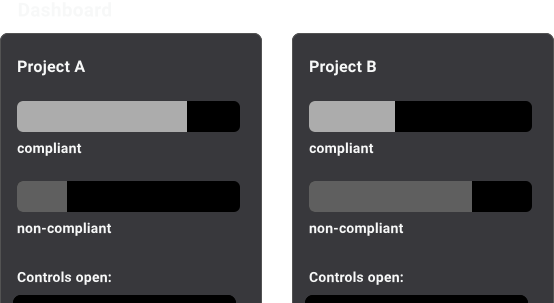
See live status with real operational context

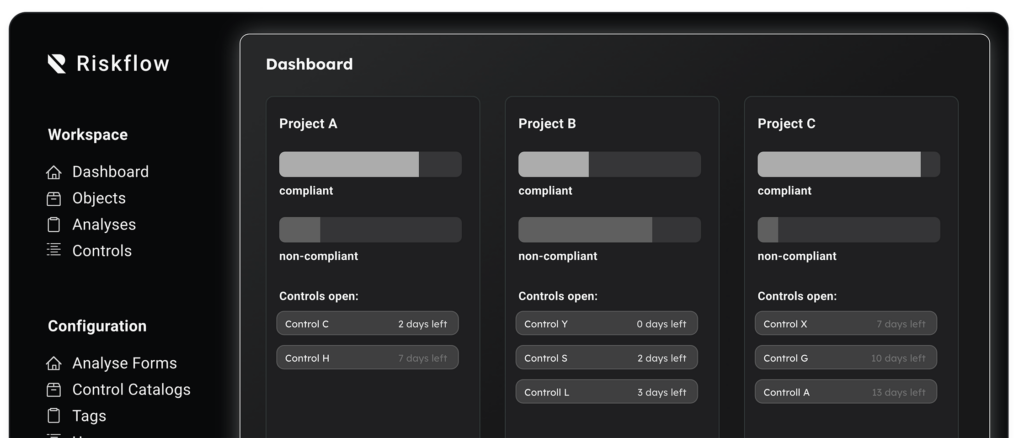
Track gaps, ownership, pending work, and current control status in one place. Teams and management get a more current view of what needs attention.

More Features: Consistency (Draft – Publish – Archive), Audit log, Cloud or on-prem or own-cloud, Role separation

We continue to expand Riskflow Asset based on customer needs and regulatory change.

Seamless Integration

Work with the systems you already use

Riskflow Asset fits into your existing environment. Keep your operational systems where they are, bring in the context GRC needs, and turn requirements into controls, evidence, and proof in one traceable flow.


ServiceNow: Keep ServiceNow as your source of truth Sync your asset landscape from ServiceNow and keep it aligned over time. Riskflow Asset adds the requirement, control, and evidence layer on top without forcing another disconnected asset silo.

CSV import: Start with structured data you already have Bring in assets and supporting data from spreadsheets or exports when that is the fastest path. A clean import is often the easiest way to get a first workflow live.

APIs: Connect Riskflow Asset to your stack Use APIs to extend Riskflow Asset into your existing processes and data flows. That keeps your setup flexible as your control environment grows.

Integration principle: Integrate, don’t replace

Riskflow Asset is built to work with your existing systems, not to compete with them. Your source systems stay operational. Riskflow Asset adds traceable control logic, workflow, and proof on top.

Any Questions?

Riskflow Asset connects requirements, asset context, controls, and evidence in one traceable flow. Instead of treating GRC as disconnected questionnaires and documentation, it helps teams see what applies, what is missing, and what is proven.

Governance, Risk, and Compliance (GRC) is the work of turning regulatory, legal, contractual, and internal requirements into clear ownership, effective controls, and verifiable evidence.

Riskflow Asset is especially suited to banks, regulated fintechs, insurers, and critical service providers. It also fits other audit-heavy teams with strong governance, control, and evidence requirements.

Riskflow Asset helps teams operationalize regulatory, legal, contractual, and internal requirements by translating them into clear control scope, ownership, assessments, and proof.

No. Keep your existing source systems. Riskflow Asset is designed to use asset context from systems such as ServiceNow, CSV-based imports, and APIs instead of forcing another redundant asset database.

Yes. Riskflow Asset is built to fit into existing environments through ServiceNow integration, CSV import, and APIs. The goal is to work with your stack, not replace it.

That depends on your environment and scope, but teams can often start with a focused workflow, existing data, and reusable templates rather than a large replacement project.

By connecting requirements, context, controls, and evidence in one flow. Teams can reuse structure, inherited context, and shared control responses instead of rebuilding the same logic across audits and review cycles.

Riskflow Asset keeps the path from requirement to control to evidence traceable. That makes it easier to show what applies, what was assessed, what was evidenced, and what still needs action.

Yes. Riskflow Asset supports cloud, on-prem, and own-cloud deployment models for teams that need flexibility in how they operate the platform.

Riskflow Asset is built for environments that care deeply about privacy, auditability, and operational control. Security, access control, and deployment flexibility are treated as core requirements, not add-ons.

Riskflow Asset is built to stay usable as complexity grows. Teams can work across large asset landscapes and control environments without losing structure or traceability.

Know what applies. See what’s missing. Prove what’s done.

Riskflow Asset gives regulated and audit-heavy teams a clear view across assets, controls, and evidence – without another disconnected GRC silo.